
Five frameworks ask the same underlying question in different words: what is connected to your network, and how do you know what it is? Most compliance teams answer it five separate times, in five documents on five timelines. Here is what answering it once looks like.
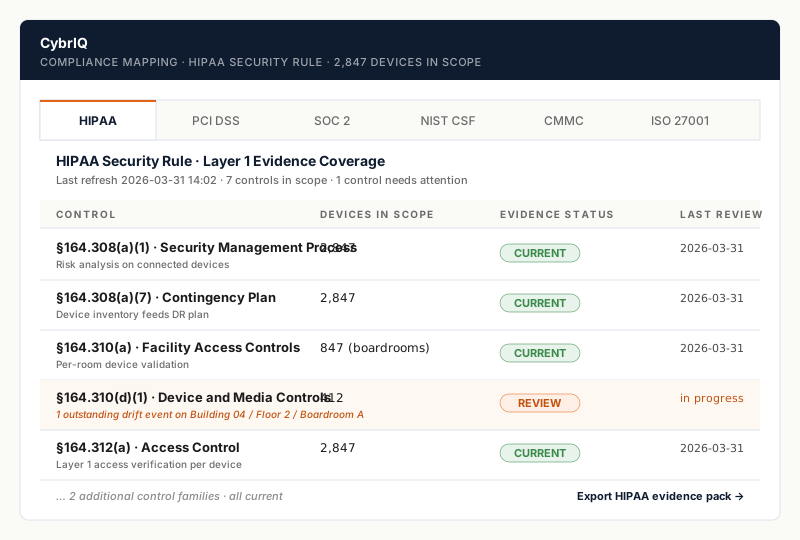
The five-report problem.
Most regulated enterprises are in scope for several frameworks at once. A Fortune 500 healthcare system answers to HIPAA for patient data, PCI for payment processing in the cafeteria and pharmacy, SOC 2 for the customer-facing platform, NIST CSF for the federal contracts unit, and CMMC for any defense-adjacent work. One network. Five audits.
For decades the workaround has been to rebuild the inventory five times. Each audit team gets a spreadsheet of its own, with an evidence package and a scope definition to match. Every input comes from the same network, yet the outputs look different enough that nobody inside trusts them to reconcile.
What each framework asks for.
Strip away the formatting and the underlying control is close to identical: maintain a current inventory of connected assets and demonstrate that the controls protecting them have operated continuously over the audit period. Here is how the five frameworks put it:
- HIPAA Security Rule §164.310(d)(1) Device and media controls. §164.308(a)(1)(ii)(D) information system activity review. The covered entity must implement controls over devices that contain electronic protected health information and review records of activity routinely.
- PCI DSS 4.0 Requirement 12.5.1: maintain an inventory of system components in scope for PCI DSS, including a description of function or use. Requirement 1.2.4: configurations of NSCs are reviewed at least every six months.
- SOC 2 (TSC) Common Criteria CC6.1: logical and physical access controls restrict access to information assets. CC7.1: detection mechanisms identify configuration changes that could result in vulnerabilities. CC8.1: change management is governed and recorded.
- NIST CSF 2.0 ID.AM-01: inventories of hardware managed by the organization are maintained. ID.AM-02: inventories of software, services, and systems managed by the organization are maintained. PR.PS-02 / PR.IR-01: configurations are managed; networks and environments are protected.
- CMMC Level 2 AC.L2-3.4.1: establish and maintain baseline configurations and inventories. AC.L2-3.4.2: establish and enforce security configuration settings. CM.L2-3.4.7: restrict, disable, or prevent the use of nonessential programs, functions, ports, protocols, and services.
One record satisfies all of them.
Put the controls side by side and the duplication is obvious. Each one wants the same source data: a dated, authoritative record of what is connected right now, with evidence that each connection was verified and that drift from the baseline gets caught.
CybrIQ produces that record once. It is kept per device and per port, rolled up by building, refreshed continuously and dated to the second. A HIPAA auditor, a PCI assessor, a SOC 2 firm, a federal NIST reviewer and a CMMC C3PAO can each pull the slice that satisfies their framework, and nobody rebuilds the inventory underneath.
What changes for the GRC team.
Three jobs go away:
- The pre-audit reconstruction project. The artifact the auditor wants is already current, so nobody assembles it the week before fieldwork.
- The five-spreadsheet maintenance burden. The mapping document ties each framework's controls to slices of one record. A new framework adds mapping rows. It does not add a spreadsheet.
- The reconciliation theater. If the HIPAA inventory and the PCI inventory disagreed last quarter, both were probably wrong. With one underlying record they cannot disagree.
The auditor's side of it.
Audit firms increasingly distinguish between evidence assembled for them and evidence that exists because the platform produces it continuously. The first is a deliverable. The second is a control. The auditor's risk model treats them differently, and most audit firms have started to price the difference: continuous evidence shrinks fieldwork hours, and assembled evidence does not.
For the audit team, a continuous Layer 1 record means the inventory is current as of the moment they pull it. Drift events arrive already triaged and dated. Each control they test has a pre-mapped evidence slice waiting. Findings in the inventory category go to zero, because there is no longer a rebuild window in which the inventory can be wrong.
Five frameworks ask one question. CybrIQ produces the record once, and the GRC team maps it to whichever framework the audit reports against. For customers who want the work done for them, ComplianceIQ runs the program.
Further reading
- The asset register lies. How the spreadsheet falls behind the wire on day one and stays behind.
- "Looks good" is not Layer 1 evidence. What a control-room dashboard shows, what an auditor needs instead, and where the two part ways.
Map one record to every framework you report against.
ComplianceIQ pairs CybrIQ's continuous Layer 1 evidence with running the audit program itself. Controls come pre-mapped for all five frameworks above. Others on request.