
- Home
- CrossConnect
- Modules
- Notary
Notary
Can we hand an auditor the evidence behind our controls?
Explore NotaryAn audit request, customer review, or internal control review needs evidence on a short timeline.
Control records are spread across systems, leaving the team to assemble the audit trail by hand.
The audit request arrives with a short deadline. Notary assembles the records the team already holds into a dated, control-by-control evidence pack.
Give the reviewer a dated view of the records already held.
- Organize current records into a control-by-control evidence pack.
- Include configuration analysis, LLDP, forwarding, configuration-drift, and audit-chain context when those records are available.
Turn available records into a dated evidence pack.
- Builds a control-by-control evidence pack from current records.
- Includes configuration analysis, LLDP, forwarding, audit-chain, and configuration-drift context where available.
Demo controls are loading.
Open Notary in the record.
Open the resulting view, then review the evidence and the next safe action beside it.
Segmentation and audit history in the pack
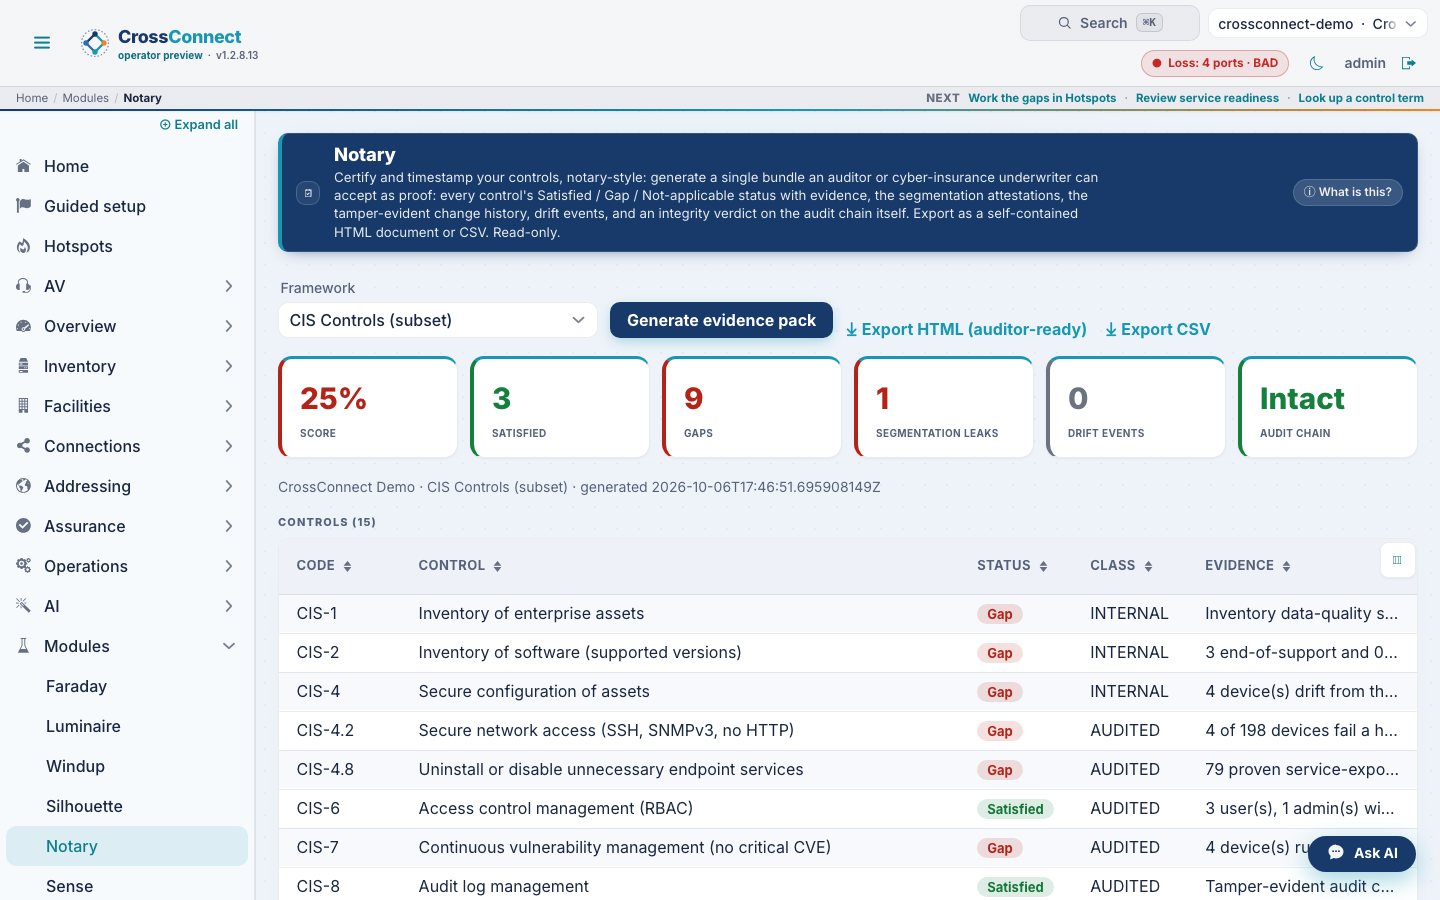
Organize current records into a control-by-control evidence pack. Include configuration analysis, LLDP, forwarding, configuration-drift, and audit-chain context when those records are available.
Evidence and interpretation
Builds a control-by-control evidence pack from current records. Includes configuration analysis, LLDP, forwarding, audit-chain, and configuration-drift context where available.
- The chosen control framework and the status recorded against each control.
- The configuration, discovery and drift records supporting a satisfied control or a reported gap.
- The evidence-pack context and audit-chain integrity associated with the exported record.
The pack remains reviewable because the control reference, source record, collection time, and any configuration drift remain together. A reviewer can trace the pack back to the current records instead of accepting a summary without its supporting context.
Investigation steps
- Start with the control the reviewer is asking about and read its recorded status.
- Trace that control to its supporting evidence and compare the record with any configuration drift.
- Use the gap or exception to identify the control owner’s next review before sharing the pack.
Verify the result
- Check that the pack covers the intended framework and that its evidence references can be followed.
- Review audit-chain integrity and source context alongside the control status before accepting the answer.
Scope of the conclusion
The pack describes available records at the time it is generated. It cannot certify controls that were never observed.